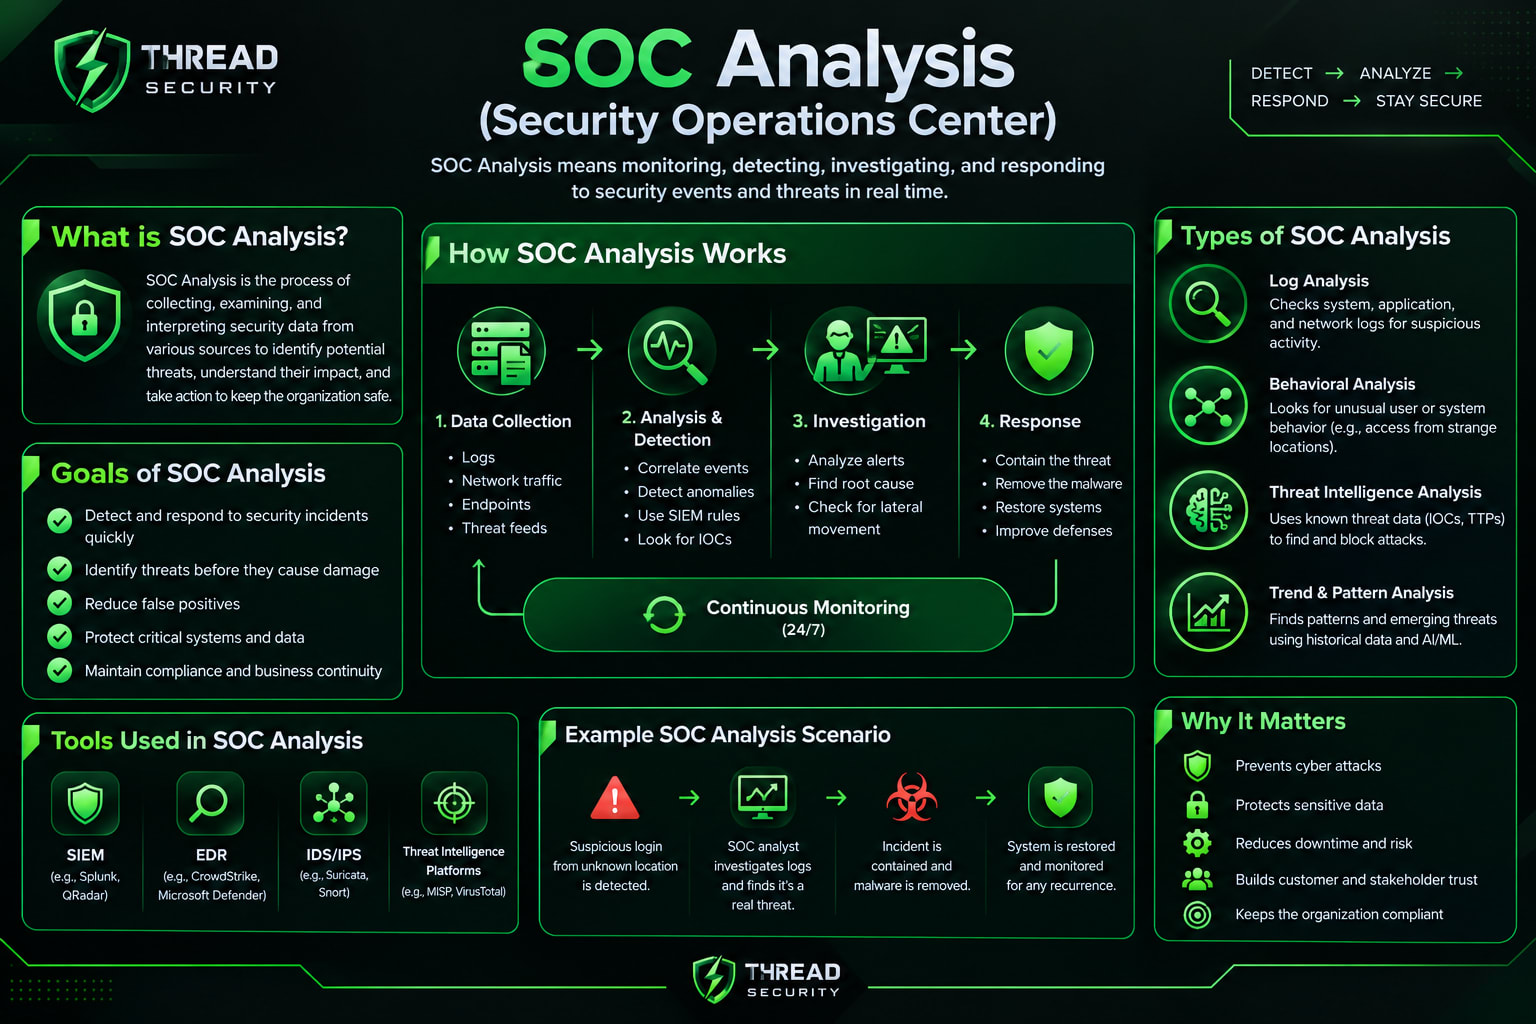
Security Operations Center (SOC) analysis is the discipline of monitoring, detecting, investigating, and responding to cybersecurity threats in real time. It sits at the heart of every mature security program, acting as the always-on defense line between an organization and its adversaries. This guide breaks down what SOC analysis actually involves, how analysts work, and what skills and tools define the role in 2025.
What Is SOC Analysis?
SOC analysis is the continuous process of collecting security telemetry, correlating it against known threats and behavioral baselines, and responding to confirmed incidents. It is both a technical function and an operational discipline — combining people, process, and technology to reduce an organization's mean time to detect (MTTD) and mean time to respond (MTTR). A SOC analyst's core responsibility is to turn raw signals — logs, alerts, network flows, endpoint events — into actionable security decisions.
The SOC Tier Structure
Most SOCs are organized into tiers, each handling a different level of complexity.
Tier 1: Alert Triage Analyst
Tier 1 analysts are the first line of defense. They monitor dashboards, review incoming alerts, validate whether an alert is a true or false positive, and escalate confirmed incidents. This role builds foundational knowledge of detection tools and incident workflows.
Tier 2: Incident Responder
Tier 2 analysts investigate escalated incidents in depth. They perform endpoint and network forensics, correlate events across multiple data sources, contain threats, and coordinate remediation. This tier requires strong analytical and investigative skills.
Tier 3: Threat Hunter / Subject Matter Expert
Tier 3 analysts proactively hunt for threats that automated tools miss. They develop detection rules, perform adversary emulation, and improve the SOC's overall detection coverage using frameworks like MITRE ATT&CK.
SOC Manager
The SOC manager oversees operations, metrics, staffing, and reporting to leadership. This role bridges technical operations and business strategy.
Core SOC Analysis Workflow
Every effective SOC follows a repeatable analysis loop.
1. Detection
Alerts are generated by SIEM rules, EDR signatures, UEBA anomalies, and threat intelligence feeds. Quality detection engineering determines how much noise the SOC must filter.
2. Triage
Analysts assess severity, context, and asset criticality. Not every alert deserves deep investigation — prioritization is essential to avoid alert fatigue.
3. Investigation
Confirmed alerts are investigated using logs, timelines, and forensic artifacts. Analysts determine scope, root cause, and impact.
4. Response
Containment, eradication, and recovery actions are executed, often through SOAR playbooks. Documentation and handoff are critical.
5. Lessons Learned
Post-incident reviews feed back into detection rules, playbooks, and training — closing the loop.
Essential SOC Tools
A modern SOC relies on a layered toolstack to detect, investigate, and respond to threats. SIEM platforms such as Splunk, Microsoft Sentinel, Elastic Security, and IBM QRadar aggregate and correlate logs. EDR and XDR tools like CrowdStrike, SentinelOne, and Microsoft Defender for Endpoint provide endpoint visibility. SOAR platforms including Palo Alto Cortex XSOAR, Splunk Phantom, and Tines automate response. Threat intelligence feeds from MISP, VirusTotal, and AlienVault OTX enrich alerts with context. Network analysis tools like Zeek, Suricata, and Wireshark capture traffic-level evidence. Case management systems such as TheHive, Jira, and ServiceNow track incidents end to end.
MITRE ATT&CK in SOC Analysis
The MITRE ATT&CK framework maps adversary tactics, techniques, and procedures (TTPs) to real-world behavior. SOC analysts use it to build detection coverage across the kill chain, prioritize alerts based on mapped techniques, conduct gap analysis on existing detections, and communicate threat context to leadership. It is the common language that connects detection engineering, threat hunting, and incident response.
Key Metrics for SOC Performance
SOC performance is measured through quantifiable metrics. Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR) measure speed. The alert-to-incident ratio measures detection quality. False positive rate measures analyst workload efficiency. Coverage percentage measures how many ATT&CK techniques the SOC can detect. Tracking these metrics allows SOC managers to identify bottlenecks and demonstrate value to the business.
Skills Every SOC Analyst Needs
Effective SOC analysts combine technical depth with analytical thinking. Core skills include log and packet analysis, SIEM query languages such as SPL, KQL, and Lucene, networking fundamentals including TCP/IP, DNS, and HTTP, operating system internals for Windows and Linux, threat intelligence and IOC enrichment, scripting in Python and PowerShell, and a solid grounding in incident response and digital forensics.
Common SOC Challenges
SOC teams face persistent challenges. Alert fatigue from excessive false positives drains analyst attention. Burnout and high turnover erode institutional knowledge. Tool sprawl and integration gaps create blind spots. A shortage of skilled Tier 2 and Tier 3 analysts limits depth. And detection rules age quickly against evolving adversary tradecraft.
The Future of SOC Analysis
AI and automation are reshaping SOC workflows. Machine learning reduces triage load, SOAR automates response, and UEBA surfaces threats that signature-based tools miss. The analyst of the future will spend less time on manual review and more time on threat hunting and detection engineering. Human judgment remains irreplaceable, but it will be amplified by intelligent tooling.
Conclusion
SOC analysis is a demanding but rewarding discipline. Mastering the tier structure, workflow, tooling, and frameworks like MITRE ATT&CK gives analysts the foundation to detect and respond to real threats with confidence. Whether you are starting as a Tier 1 triage analyst or refining Tier 3 hunting skills, the principles remain the same: observe, analyze, respond, and improve.
Atish Chand
VERIFIEDFaculty Mentor · Thread Security
Faculty mentor & research guide at Thread Security Education.