How to Become an Ethical Hacker in India is a common question among students, IT graduates, and career changers interested in cybersecurity. Ethical hacking involves assessing the security of computer systems, networks, and applications with proper authorisation to identify weaknesses before malicious actors can exploit them. It combines technical knowledge, investigative thinking, documentation, and respect for the law. You do not need to master every hacking tool on day one. A stronger starting point is to understand how technology works, practise in controlled environments, and learn how to report security issues responsibly.
This guide explains the ethical hacking roadmap for beginners in India, including essential skills, useful certifications, practical projects, potential job roles, and legal considerations. It is educational guidance, not a promise of employment or legal advice.
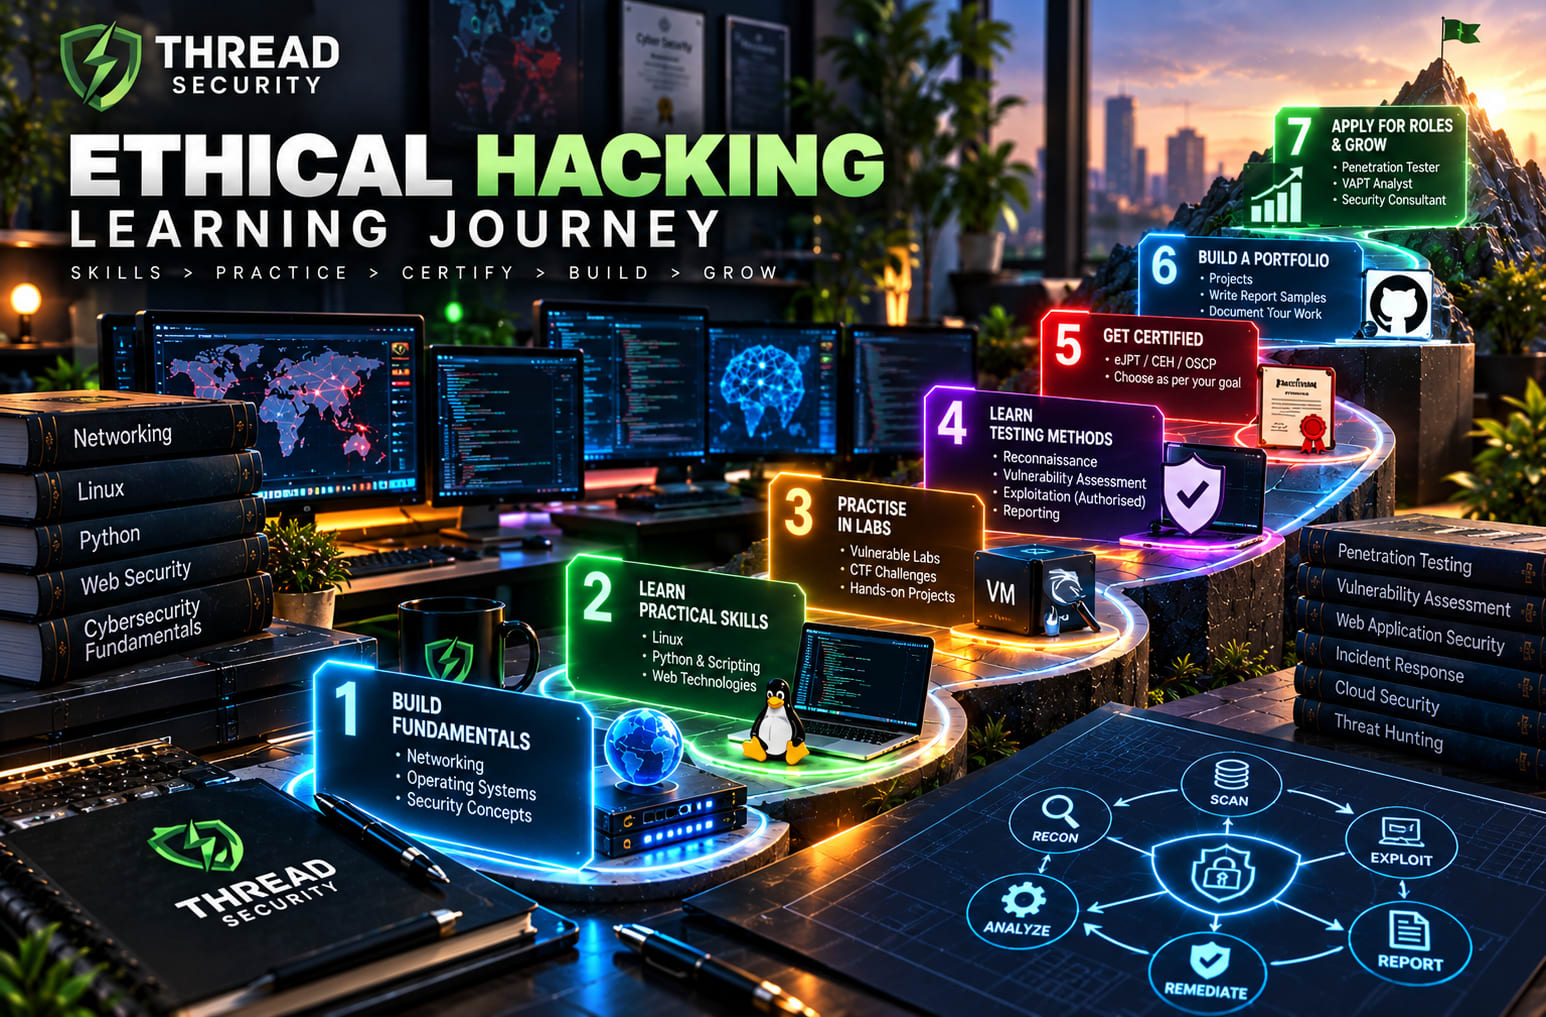
1. What Does an Ethical Hacker Do?
An ethical hacker performs security testing within an agreed scope to help an organisation understand and reduce its exposure to cyber risks. Depending on the role, the work may include reviewing web applications, testing network configurations, assessing access controls, validating security patches, and documenting vulnerabilities.
Ethical hackers may work as penetration testers, vulnerability assessment analysts, application security testers, security consultants, or members of a broader security team. These roles overlap, but they are not identical. Vulnerability assessment commonly focuses on identifying and prioritising weaknesses, while penetration testing attempts to validate how far a defined attack path could go under approved conditions.
The professional standard is not simply finding a vulnerability. It is testing safely, collecting appropriate evidence, explaining the risk clearly, and helping the owner fix the issue.
2. Build the Foundations Before Learning Hacking Tools
If you are a beginner, start with the technology that security tools examine. Without foundational knowledge, tool output can be confusing and easy to misinterpret.
Networking fundamentals
Learn IP addressing, subnetting, ports, TCP and UDP, DNS, HTTP and HTTPS, routing, firewalls, and common network services. Understand what happens when a browser connects to a website and how traffic moves between devices. Wireshark can help you inspect packet captures from your own lab or authorised training exercises.
Linux and Windows
Learn directory structures, permissions, users and groups, processes, services, logs, and command-line operations. Practise with a Linux distribution and become comfortable with basic shell commands. Windows knowledge is equally useful because business environments frequently depend on Windows endpoints, identity systems, and servers.
Programming and scripting
Python is useful for automating repetitive tasks, processing logs, and working with APIs. Basic JavaScript helps when assessing web applications, while SQL knowledge helps you understand database queries and common application security mistakes. You do not have to become an expert software developer before beginning security studies, but you should learn to read code and understand how applications handle input, authentication, and data.
Security concepts
Study authentication, authorisation, encryption, hashing, least privilege, secure configuration, patch management, threat modelling, and vulnerability management. Learn the difference between a vulnerability, a threat, an exploit, and a security risk. These concepts help you explain why a technical weakness matters to the organisation responsible for the system.
3. Follow a Practical Ethical Hacking Roadmap
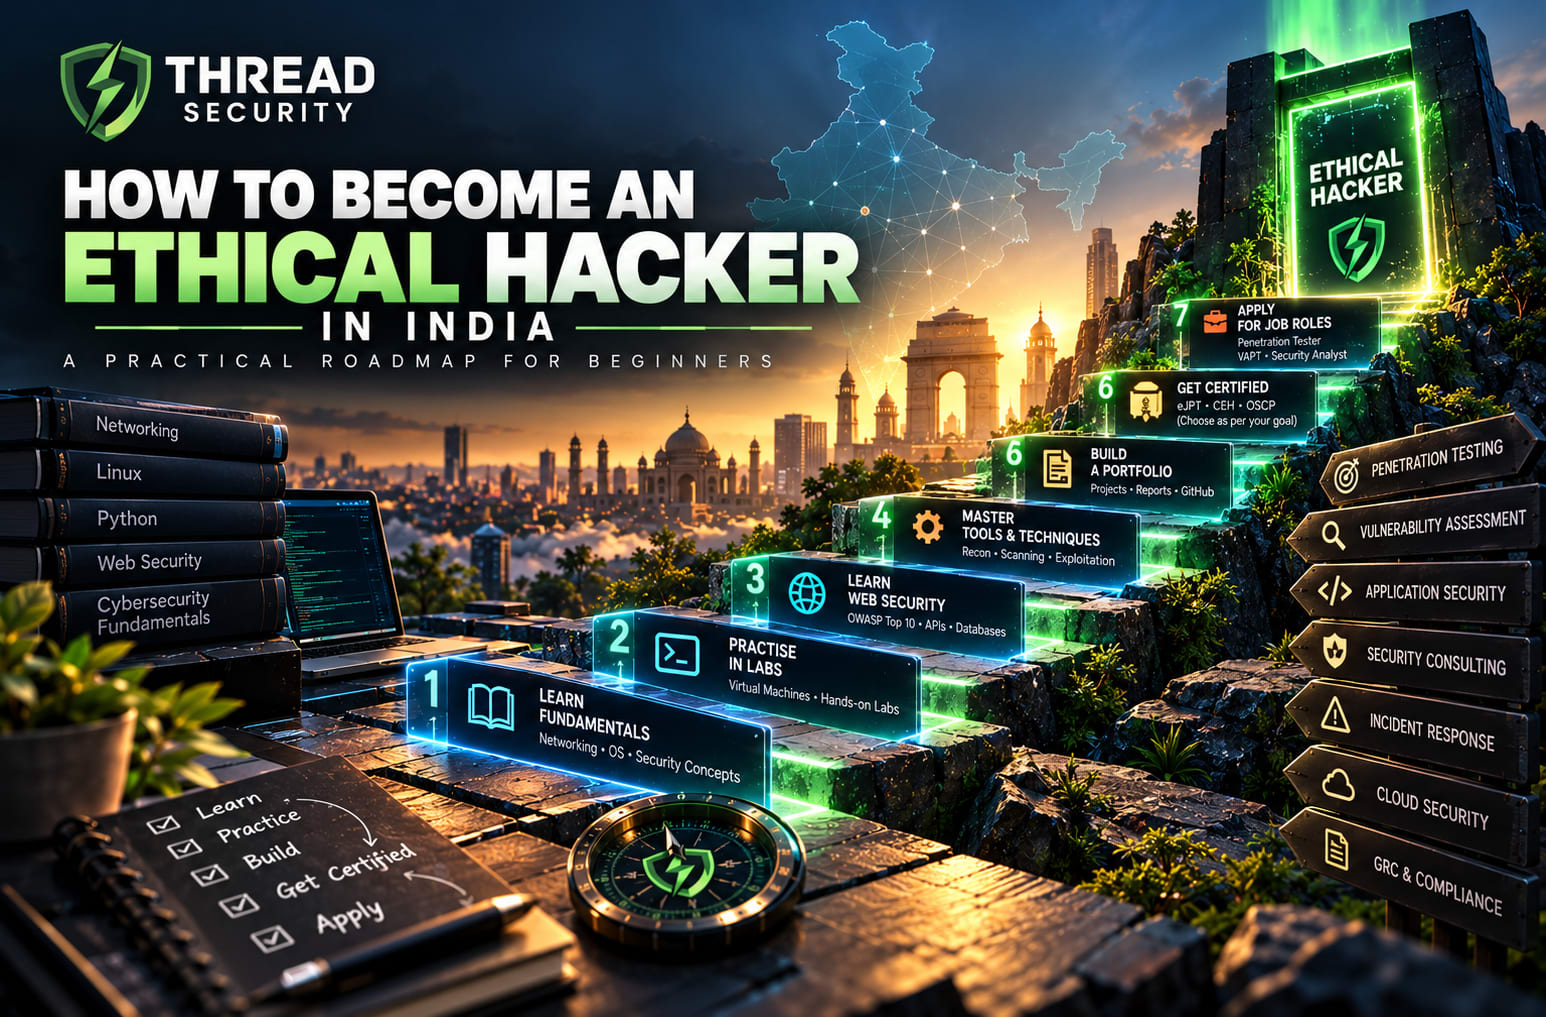
A structured learning plan is more useful than installing many tools without understanding their purpose. The following stages provide a flexible starting point; the time required will depend on your existing knowledge and the hours you can practise each week.
Stage 1: Learn IT and networking
Begin with operating systems, networking, web technologies, and command-line skills. Recreate small networks using virtual machines and practise troubleshooting connectivity. Your goal is to explain what a service does and how to investigate a problem, rather than memorising commands.
Stage 2: Learn web and application security
Understand requests, responses, cookies, sessions, access controls, APIs, and database interactions. Use the OWASP Top 10 as a starting point for learning important web application security risks. Explore each topic in an intentionally vulnerable application designed for training, not against a real website without permission.
Stage 3: Practise in authorised labs
Use controlled environments such as PortSwigger Web Security Academy, OWASP Juice Shop, and other deliberately vulnerable training applications. These environments let you learn testing methods without putting real users or systems at risk. Read the lab instructions, take notes, and explain the underlying weakness in your own words.
Stage 4: Learn a repeatable testing process
Practise defining the scope, identifying assets, gathering permitted information, checking for weaknesses, validating findings safely, and writing a report. Learn when to stop testing. If a finding could expose personal information, disrupt a service, or affect systems outside the agreed scope, do not continue without explicit approval.
Stage 5: Build a portfolio and prepare for roles
Document completed labs, defensive fixes, small security scripts, and sample vulnerability reports. Remove secrets, private data, and identifying details from anything you publish. A good portfolio explains the problem, your authorised testing method, the evidence, the impact, and the recommended remediation. Employers can then assess your reasoning instead of seeing only a list of tools.
4. Essential Tools to Learn
Learn tools in the context of a specific security task. Kali Linux is a Linux distribution that includes many security-testing utilities; installing it alone does not make someone a penetration tester.
Nmap: Learn service discovery and port scanning on systems you own or are explicitly authorised to assess.
Wireshark: Inspect network packets and understand communication protocols using permitted traffic captures.
Burp Suite: Understand how web requests and responses can be examined during authorised application testing.
OWASP ZAP: Explore web application security testing in a lab or approved environment.
Linux command line: Practise file handling, permissions, process inspection, and basic automation.
Git and Python: Maintain a portfolio, version your scripts, and automate safe, repeatable tasks.
Tool availability and features can change, and different organisations use different technology stacks. Learn the testing concept first so that you can adapt when a team uses a different product.
5. Which Ethical Hacking Certifications Should You Consider?
Certifications can provide structure and help demonstrate knowledge, but they are not a substitute for hands-on practice. Choose a credential according to your current level, target role, budget, and the certification provider's latest requirements.
Entry-level cybersecurity certification
The ISC2 Certified in Cybersecurity (CC) is positioned as an entry-level credential and does not require previous work experience. Its published domains include security principles, governance, identity and access management, networking and cloud security, and security operations and incident response. It can help beginners organise their foundational studies.
CompTIA Security+
Security+ is another widely known general cybersecurity certification. Review the current exam objectives and recommended experience on the official CompTIA website before deciding whether it matches your preparation and career goals. It covers broader security concepts rather than serving only as a practical penetration-testing qualification.
Certified Ethical Hacker (CEH)
EC-Council's Certified Ethical Hacker credential is specifically associated with ethical hacking. Before enrolling, check the official certification page for the current exam, eligibility routes, training requirements, fees, and any experience criteria that apply to your chosen route. Do not rely on an old course advertisement for current certification rules.
Practical certifications and training
Some learners later choose practical, role-specific training in penetration testing or web application security. Compare the assessment format, lab access, renewal conditions, total cost, and employer relevance. You do not need to collect every certification. A sensible path is to learn the foundations, complete practical exercises, and select credentials that support a clear career goal.
6. Build Projects That Demonstrate Real Understanding
A beginner can create a meaningful portfolio without testing public targets. Consider these project ideas:
Home lab: Set up isolated virtual machines and document how you configure and secure them.
Web security lab report: Complete an intentionally vulnerable training exercise and write a report describing the weakness and remediation.
Security header checker: Write a small script that checks security headers on a local application or an explicitly authorised target.
Log analysis project: Parse sample authentication logs and identify repeated failed logins or unusual patterns.
Secure configuration checklist: Compare a test system against a recognised hardening guide and document the gaps.
Publish only work you are permitted to share. Never upload credentials, tokens, private reports, client data, or exploit details that could expose a real organisation. If you use a public training platform, follow its rules for sharing solutions.
7. Career Options and Applying for Jobs in India
Depending on your skills and experience, relevant starting roles may include junior security analyst, vulnerability assessment trainee, security operations centre (SOC) analyst, junior penetration tester, or application security intern. Job titles and requirements vary between employers, so read individual job descriptions rather than assuming every role has the same entry criteria.
Prepare a focused resume that lists technical foundations, labs, projects, certifications, and clear examples of your work. Be ready to explain what a vulnerability means, how you validated it in a permitted environment, how you judged severity, and how you would recommend fixing it. Honest documentation of what you know is more valuable than claiming expertise in tools you have barely used.
Networking with practitioners, attending security events, contributing to legitimate open-source projects, and applying for internships can help you learn about opportunities. No certification, course, or portfolio guarantees a job or a particular salary. Progress depends on practical ability, communication, employer requirements, and the opportunities available at the time.
8. Legal Rules Every Ethical Hacker in India Should Understand
Authorisation is a core requirement of professional ethical hacking. A website being publicly accessible, a device being connected to the internet, or a vulnerability being easy to reproduce does not by itself grant permission to test it.
Information Technology Act, 2000
Section 43 of India's Information Technology Act addresses unauthorised acts involving computer systems and resources, including access, data copying, damage, and disruption, and provides for compensation in the circumstances covered by the provision. Section 66 addresses acts referred to in Section 43 when done dishonestly or fraudulently and sets out criminal penalties. The application of any provision depends on the facts and applicable law; this summary is not a substitute for legal advice.
Written permission and scope
Before conducting a professional assessment, obtain written authorisation from someone empowered to approve the work. Agree on the target systems, testing window, permitted methods, excluded assets, data-handling requirements, emergency contacts, and reporting process. A bug bounty programme or responsible disclosure policy must be read carefully because permission is limited by its stated rules.
Responsible testing and reporting
Avoid accessing, retaining, or sharing data that is not necessary to demonstrate an issue. Do not disrupt services, bypass agreed restrictions, or test third-party systems outside the approved scope. Stop and contact the designated owner if an unexpected sensitive exposure or operational risk occurs. Keep evidence proportionate, protect reports, and follow the agreed disclosure timeline.
CERT-In directions
The Indian Computer Emergency Response Team (CERT-In) publishes official directions and guidance concerning cybersecurity practices and incident reporting. Its directions dated 28 April 2022 include specified incident-reporting obligations and logging requirements for covered entities. These are organisational obligations, not a blanket licence for individuals to perform security testing. Review the official directions and FAQs to understand which requirements apply to a particular organisation or engagement.
Rules and regulatory requirements can change, and contractual duties may also apply. For an actual assessment, check current primary sources and obtain qualified legal guidance when the scope or permission is uncertain.
9. Common Mistakes Beginners Should Avoid
Running scanning tools against public IP addresses or websites without permission.
Memorising commands without learning the underlying network or application behaviour.
Assuming that a certificate alone proves practical competence.
Publishing screenshots or reports that expose real data, credentials, or customer details.
Ignoring remediation, communication, and report writing.
Paying for expensive training before reviewing the syllabus, lab quality, and certification requirements.
Claiming that a tool found a confirmed vulnerability without validating the evidence safely.
Ethical hacking is a discipline of methodical testing and responsible disclosure. Curiosity is valuable, but it must be paired with restraint, documentation, and permission.
10. How Thread Security and Thread Security Education Fit Into Your Roadmap
Building a cybersecurity career takes more than learning commands from isolated tutorials. Learners benefit from a structured path that connects networking, operating systems, web security, vulnerability assessment, reporting, and responsible testing. Thread Security works in the cybersecurity space, while Thread Security Education focuses on cybersecurity learning and skill development. For learners exploring ethical hacking, these areas align with the broader goal of building a foundation in security concepts and applying them through guided, authorised practice. Review the available learning options and course details directly, and choose training that matches your level, objectives, and budget. As with any training provider, confirm the current syllabus, practical components, instructor support, fees, and outcomes before enrolling.
Conclusion: Start With Fundamentals, Then Practise Responsibly
The roadmap to becoming an ethical hacker in India begins with networking, Linux, programming basics, and security principles. From there, practise in legal labs, learn a repeatable testing process, document projects, and choose certifications that support your goals. Develop the habit of explaining vulnerabilities clearly and recommending realistic fixes. Most importantly, understand the legal boundaries: professional security testing requires appropriate permission and must remain within the agreed scope.
Official Resources and Further Reading
OWASP Juice Shop — intentionally vulnerable training application
ISC2 Certified in Cybersecurity — official certification details
Ready to take your next step in cybersecurity? Explore the learning opportunities available through Thread Security Education and learn more about Thread Security. Continue reading our cybersecurity resources, strengthen your technical foundations, and build practical skills through authorised labs and well-documented projects. Start with one topic, practise it responsibly, and keep learning—your journey toward a cybersecurity career begins with consistent, ethical work.
Akshay Kumar
VERIFIEDAcademic Coordinator · Thread Security
Faculty mentor & research guide at Thread Security Education.