Cybersecurity is a hands-on discipline, but the cost of entry can feel intimidating. Commercial labs, certification subscriptions, and enterprise-grade hardware quickly add up. The good news: you can build a free cybersecurity lab on a single laptop, and a disciplined learner can build real, job-relevant skills without spending more than the cost of an internet connection. This roadmap shows you how to set up a free, safe, and legal practice lab from the ground up.
Why a Free Lab Works
Skill in security comes from repetition against realistic scenarios not from expensive equipment. Virtualization lets you run entire networks on a single laptop. Community platforms provide legal targets and guided challenges. Open-source tools match the enterprise products analysts use daily. What matters is structure: a deliberate progression from fundamentals to offense to defense, with each step reinforcing the last.
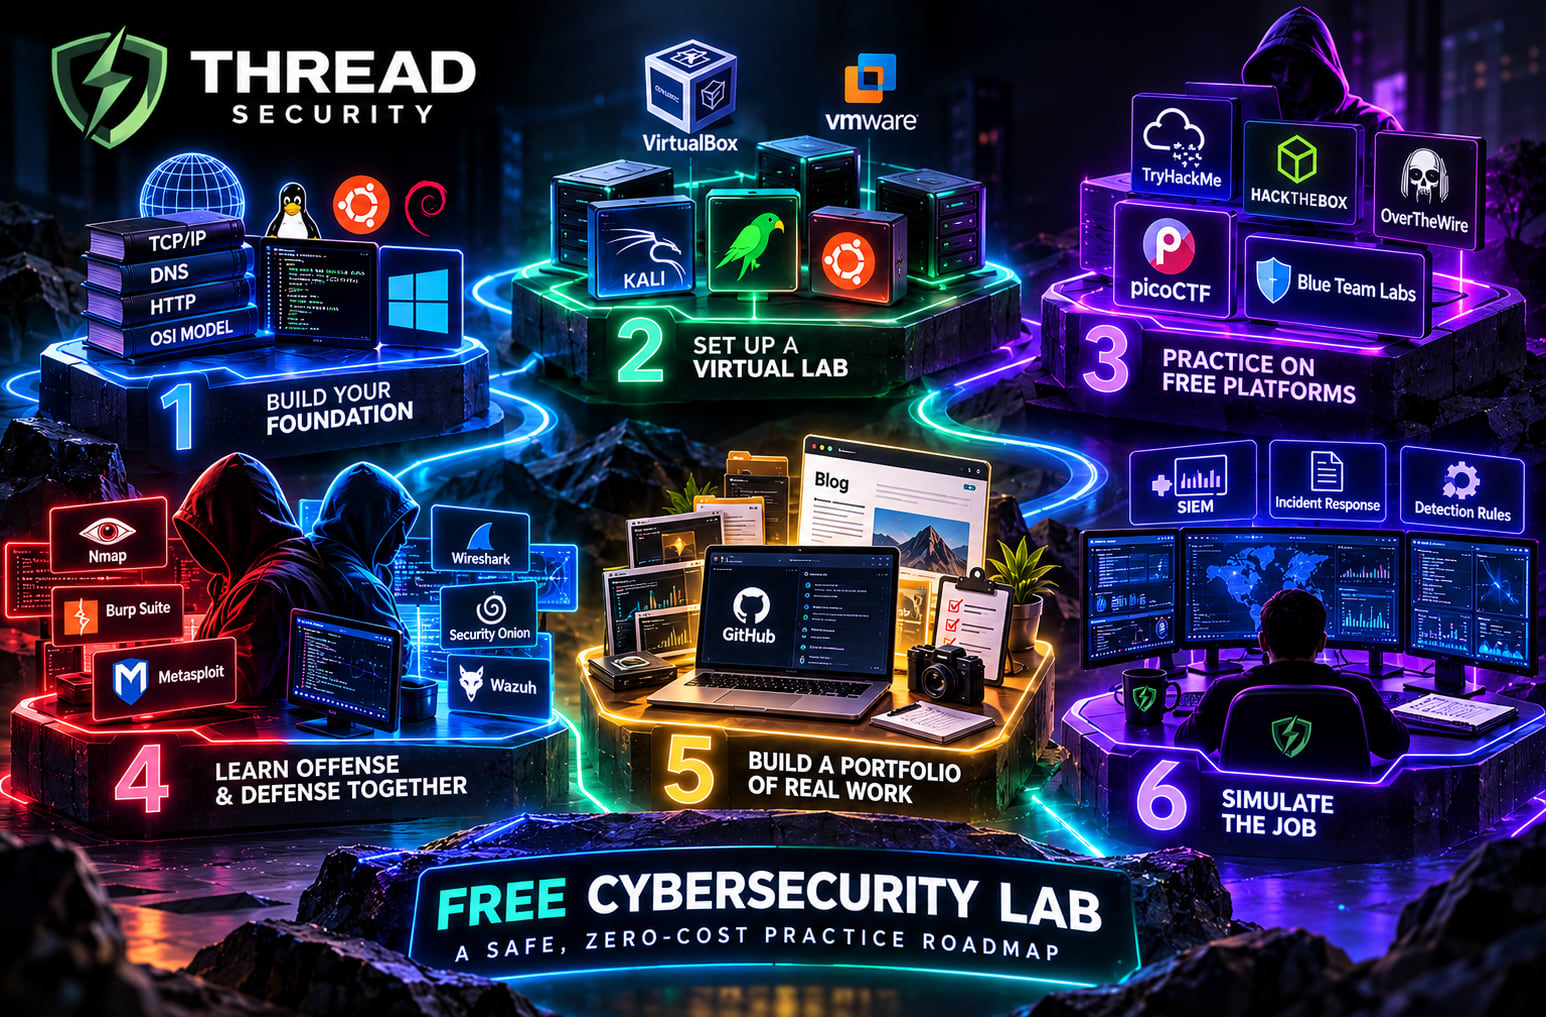
Step 1: Build Your Foundation (Weeks 1–4)
Before touching a single security tool, get comfortable with the basics. Learn TCP/IP, DNS, HTTP, and the OSI model. Practice on Linux install a free distribution like Ubuntu or Debian and learn the command line, file permissions, and process management. Study Windows internals: registry, services, event logs, and user accounts. Free resources include Cisco Networking Academy's Skills for All, Professor Messer's Network+ videos, and Linux Journey. Do not skip this step; security tools assume fluency in these fundamentals.
Step 2: Set Up a Virtual Home Lab (Free)
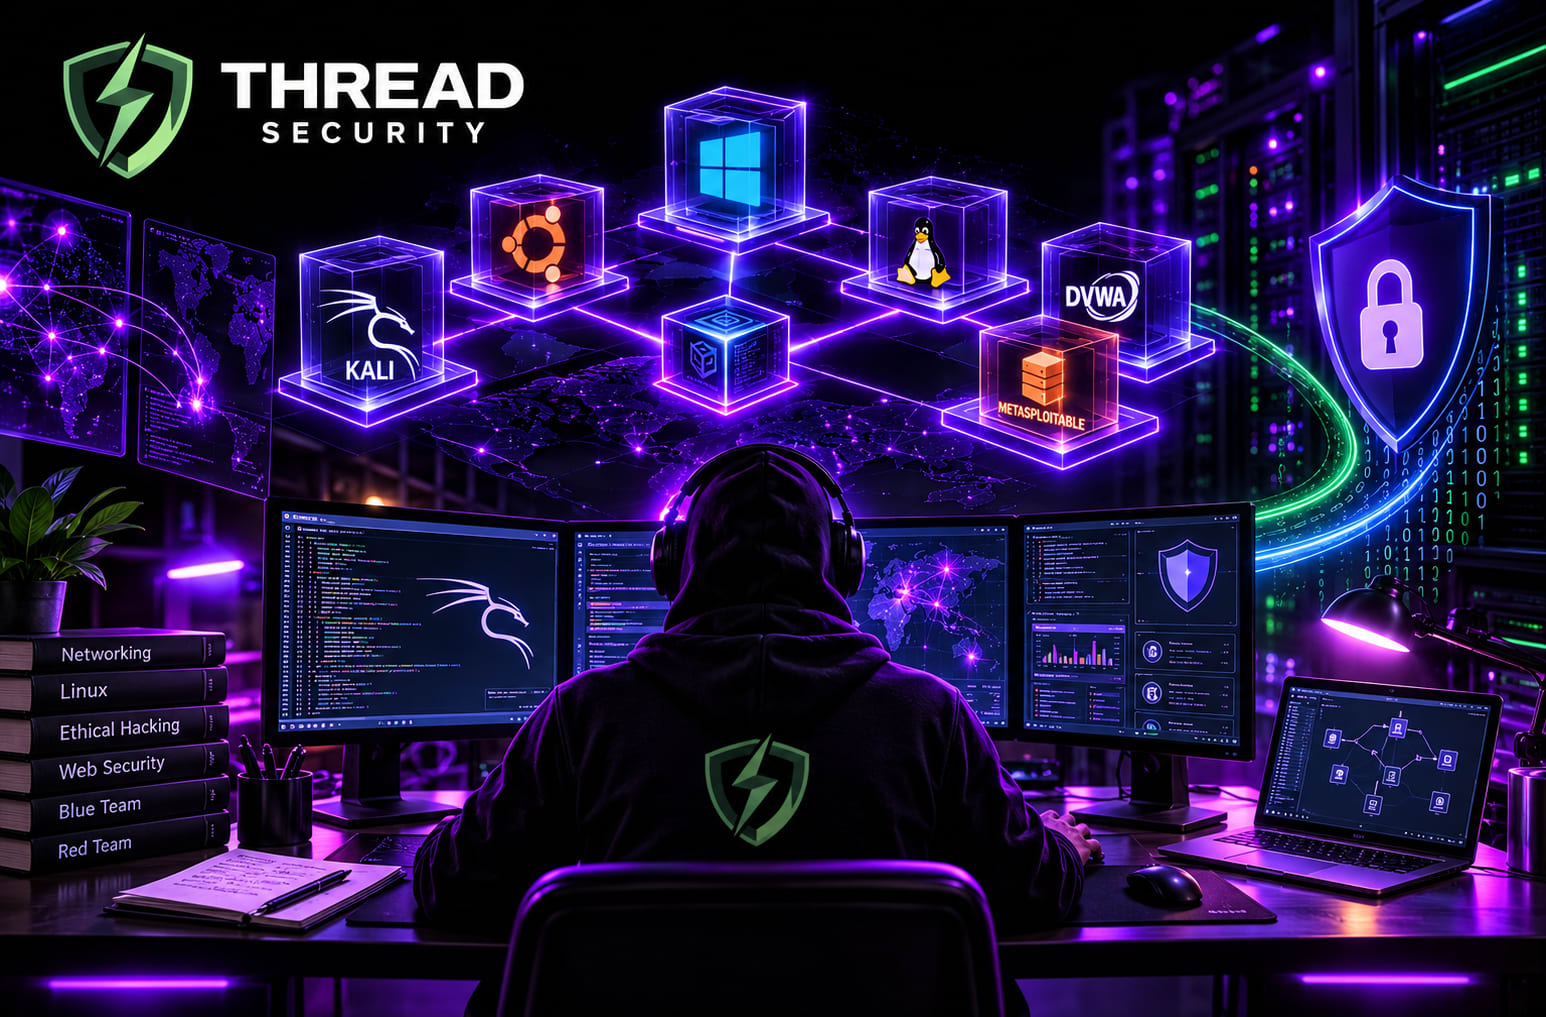
Install VirtualBox or VMware Workstation Player both free. Download Kali Linux or Parrot OS for offensive work and Ubuntu Server for building targets. Create an isolated internal network so your lab VMs can talk to each other without exposing your home network. Snapshots let you break things and roll back instantly. For lighter hardware, use Docker containers instead of full VMs. A modest 8GB RAM laptop can comfortably run two to three lightweight VMs at once.
Recommended Free Lab Stack
VirtualBox or VMware Player for the hypervisor. Kali Linux or Parrot OS as your offensive workstation. Metasploitable 2 or DVWA (Damn Vulnerable Web Application) as practice targets. OWASP Juice Shop for web application testing. Security Onion or a lightweight Elastic stack for blue team log analysis. Wireshark for packet inspection. All of these are free, open-source, and widely used in real security work.
Step 3: Practice on Legal, Free Platforms (Weeks 5–12)
The fastest way to build skill is against curated challenges with guidance. TryHackMe offers free rooms covering networking, Linux, web exploitation, and defensive analysis. Hack The Box has a free tier with beginner-friendly machines and its Academy introductory modules. OverTheWire's Bandit wargame teaches Linux command line through progressive puzzles. PicoCTF is free and beginner-friendly, with a strong educational design. Blue Team Labs Online and CyberDefenders provide free defensive challenges using real forensic artifacts.
Step 4: Learn Offense and Defense Together
Do not silo your learning. Offensive practice teaches you how attacks work, which directly improves your defensive intuition. On the offense side, practice reconnaissance with Nmap, web testing with Burp Suite Community Edition, and exploitation inside your isolated lab. On the defense side, analyze logs in Wireshark and Elastic, investigate Windows event logs, and triage alerts from free SIEM options like Security Onion or Wazuh. Every attack you run should be followed by the question: how would a defender detect this?
Step 5: Build a Portfolio of Real Work
Document everything. Write short walkthroughs of rooms you complete, home lab builds, and detection exercises. Publish them on GitHub or a blog. Capture screenshots of packet captures, log queries, and sanitized dashboards. A portfolio of honest, well-documented practice signals far more competence to employers than a certificate alone. It also forces you to articulate what you learned, which cements the skill.
Step 6: Simulate the Job
Real security work is repetitive, process-driven, and documented. Practice that rhythm. Set up a small SIEM, ingest logs from a target VM, and write detection rules for common techniques. Triage the resulting alerts and write incident notes. Run a tabletop exercise against your own lab: simulate a phishing incident, walk through containment, and document lessons learned. This habit of writing and reasoning about detections is what separates hobbyists from professionals.
Free Tools Worth Mastering
Nmap for network discovery. Wireshark for traffic analysis. Burp Suite Community Edition for web testing. Metasploit Framework for exploitation practice in your lab. Wazuh or Security Onion for log monitoring and detection. Zeek and Suricata for network security monitoring. TheHive for case management. Python and Bash for automation. All of these are free and used in production environments. Mastering even half of them well is more valuable than collecting dozens of shallow tool exposures.
Legal and Ethical Guardrails
Only practice on systems you own or platforms that explicitly authorize testing. Never scan networks you do not control, even ones that appear open. Use isolated lab networks to prevent accidental exposure. Read the terms of each CTF or platform before participating. Treat authorization boundaries as seriously as a professional would ethical judgment is part of the skill you are building, and a mistake here can end a security career before it starts.
A Realistic Weekly Schedule
Ten to fifteen focused hours per week is enough to see steady progress. Spend three hours on fundamentals, five on hands-on platform challenges, three on home lab exercises, and two on writing up what you learned. Track your progress against a simple goal list: complete a networking module, finish ten TryHackMe rooms, build one detection rule, write one walkthrough. Consistency beats intensity, and a year of steady practice produces genuinely competitive skills.
Cyber Security Courses in Jalandhar: Turn Awareness Into a Career
If you are looking for cyber security courses in Jalandhar, Thread Security Education offers programs with offline classes and live online batches. According to its website, they include a Cyber Security Course (CEH and industrial training) in 45-day and 6-month formats, Defensive Cyber Security with Blue Team and SOC operations, and Web Penetration Testing and Bug Bounty Hunting, plus AI and AI-security tracks. Fraud monitoring, payment-app security and incident response are exactly where those skills are used.
Contact: Thread Security Education, 3rd Floor, Vasal Mall, Opposite Hotel President, Police Line, Jalandhar, Punjab 144001. Phone: +91 7347398956. Email: edu@threadsecurity.in. Hours: Monday to Saturday, 9 AM to 7 PM.
Common Pitfalls to Avoid
Tutorial hell is the biggest trap watching endless videos without doing. Do not chase certifications before you can actually do the work. Avoid tool hoarding; depth beats breadth. Do not neglect documentation, and do not skip the defensive side because offense feels more exciting. Finally, do not compare your progress to viral success stories; the professionals you admire put in years of unglamorous, consistent practice.
Conclusion
A free, safe, well-structured lab is enough to build real cybersecurity skill. Start with fundamentals, stand up a virtual lab, practice on legal platforms, and document everything. Treat every offensive exercise as a detection opportunity, and treat authorization boundaries as sacred. The tools are free, the platforms are free, and the only real investment is disciplined time. That is the whole roadmap nothing expensive required.
Call to Action
Share these five habits with a parent or relative today and agree on a family rule for unexpected payments. If your business needs its payment flows tested, see threadsecurity.org. To build a career in cyber security in Jalandhar, see Thread Security Education.
Simranjit Kaur
VERIFIEDAI Trainer · Thread Security
Faculty mentor & research guide at Thread Security Education.